Hoax threats and frozen fridges disrupt Europe
Twenty-five flights faced false alarms while cyber attacks targeted blood banks and supermarket chillers across four nations.
By Tomas Rahman ·
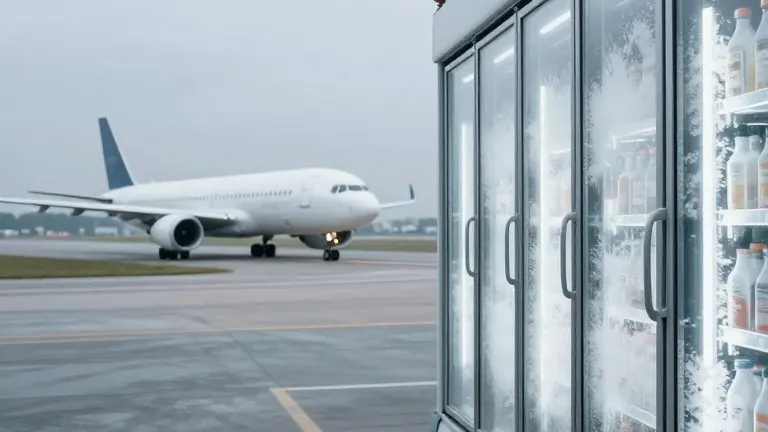
European airports and retail networks faced a week of coordinated disruptions as false bomb warnings grounded aircraft and hackers froze food supplies.
At least 25 commercial flights encountered hoax bomb threats during the period, forcing some planes to land urgently. This surge followed earlier alerts on Tuesday that caused seven other aircraft to be searched or diverted. Investigators have not yet linked the incidents to a specific state or terror group, but aviation experts note that the credible nature of the threats implies some level of coordination among the perpetrators.
The sky-based chaos occurred alongside digital strikes on supermarket refrigeration units in Belgium, Sweden, the United Kingdom, and France. The attacks extended to the cold storage facilities of France’s national blood service. In several cases, remote adjustments pushed thermostats to 50 degrees Celsius, causing stored goods and medical supplies to spoil.
Security analysts describe these events as part of a grey zone of hybrid warfare that has grown since 2022. These shadow attacks are often attributed to Russian efforts to disrupt support for Ukraine without starting a full-scale military conflict. Dan Sabbagh, a defence and security editor, stated that the threat environment has shifted since the War on Terror began, with hostile state threats rising as Islamist terrorism has receded.
The strategy relies heavily on psychological impact. Cybersecurity analyst Azeem Azhar compared the current internet security situation to the early days of the pandemic. He warned that artificial intelligence allows bad actors to find and spread system flaws rapidly. The attacks frequently target edge devices, which are connected to the internet but lack strong security processing power. This weakness was exposed in 2016 when a hacker nearly stole funds from the Bank of Bangladesh via an unsecured printer.
MI5 currently tracks about 3,000 active subjects of interest, prioritizing those who pose serious risks to life. Lower-level activities, such as online sabotage or preparation for physical disruptions, remain harder to detect due to resource constraints. The Turing Institute is now exploring methods to use artificial intelligence to secure critical infrastructure against opportunistic strikes.
Aisha Down, a global technology reporter, advised against panic, noting that every attack depends on finding a specific vulnerability. She cited Finland as an example of a nation closely monitoring these tactics, where reports to the national cybersecurity center have risen from 18,000 to 21,000 this year. This increase is partly driven by a growing criminal hacking ecosystem with loose links to the Russian state.
The UK government’s Be Ready initiative tells citizens to stockpile 72 hours of emergency supplies, including water and non-perishable food, to offset hybrid warfare threats. Security experts suggest that while disruptions are expected, they are rarely as long-lasting as physical damage to a power station might be. Defenders aim to keep the psychological impact from outweighing the actual physical damage.